Transforming Ideas into Mobile Apps

Mobile App Development Company Space To Tech

Most users will never visit your website first. They will open the app. And within the first few seconds — how fast it loads, whether it crashes, whether the interface actually makes sense on the device they are holding — they decide whether your product is worth keeping. That is the real starting point for any serious mobile app development company.

View Our Work
Space To Tech is a mobile app development agency based in India, delivering mobile app development services for startups, product teams, and enterprise clients across the US, UK, UAE, and Australia.We build for the devices real users carry — not just the ones that look good in a demo.
Global client locationsUSAUKUAEIndiaAustralia

0+

Projects Delivered

0+

Years of Experience

0+

Experts

0+

Countries

Trusted by global brands

What Does a Mobile App Development Company Actually Build?

A mobile app development company designs and builds applications for iOS, Android, and cross-platform devices, covering UI/UX design, backend integration, app store deployment, and ongoing support.

  • Native iOS & Android Development
  • React Native & Flutter Applications
  • Mobile UI/UX Design
  • Backend & API Integration
  • App Store & Play Store Submission
Mobile app development target

Mobile Products Are Connected Systems

A mobile app is more than a user interface. Modern applications depend on APIs, cloud infrastructure, authentication services, real-time data processing, and backend systems working together to deliver a seamless user experience.

Enterprise Mobile Apps Need Strong Architecture

For enterprise clients, mobile development includes security architecture, offline-first capability, MDM compatibility, user management, and scalable backend systems designed for long-term growth and reliability.

Architecture Decisions Define Future Scalability

Custom mobile app development at Space To Tech begins with architecture, not aesthetics. Decisions around native versus cross-platform development, backend structure, authentication, and data synchronization determine how the product evolves over time.

Your Business Needs More Than Just an App

Build a fast, scalable, and user-focused mobile experience that drives real growth.

Mobile App Development Services We Offer

Space To Tech delivers end-to-end mobile app development services, helping businesses build high-performance applications that drive engagement, growth, and measurable business results.

Custom Mobile App Development

When an off-the-shelf product does not fit the workflow, the user base, or the technical environment, custom mobile app development is the correct path. Space To Tech delivers custom mobile app development services with native mobile app architecture — no templates, no white-label code patched into something new.

Native iOS App Development

Native mobile app development for iOS means writing in Swift, using Apple's native frameworks, and building specifically for the way iOS handles memory, UI rendering, and device APIs. The result is an app that behaves exactly as iPhone and iPad users expect.

Native Android App Development

Android app development built for real devices — not emulator-only demos. Our android mobile application development covers Kotlin, Jetpack, and Google Play Store requirements so your android app performs consistently across OEM variations and network conditions.

Cross-Platform App Development (React Native & Flutter)

When a business needs iOS and Android coverage without funding two separate native builds, crossplatform mobile app development is the practical route. React Native and Flutter deliver a hybrid mobile application from a shared codebase.

Mobile UI/UX Design

Mobile responsive design that looks correct on one device is not the same as a well-designed mobile product. Our mobile design work covers information architecture, interaction design, Material Design 3 for Android, and Apple HIG compliance.

Mobile App Development for Startups & MVPs

As a mobile app development company for startups, we help teams build mobile app projects fast without cutting corners. From discovery to launch, we structure sprints so founders validate ideas before scaling spend.

Enterprise Mobile App Development

Enterprise mobile app development company engagements demand secure mobile backend architecture, offline-first workflows, and biometric authentication — the foundations enterprise mobile apps need before production rollout.

eCommerce Mobile App Development

An ecommerce mobile app development company must think in conversions, not screens. We build mobile apps with in-app purchases, mobile payment integration, and checkout flows tuned for the mobile devices your customers use.

Progressive Web App (PWA) Development

A web app with mobile responsive behaviour can reach users without a store install. PWA development combines installable web experiences with the speed of modern mobile development.

AI-Powered Mobile App Development

An ai app on mobile is only useful when inference, privacy, and UX work on-device and in the cloud. We integrate AI into mobile application workflows built for production, not demos.

Backend & API Integration for Mobile

Every serious mobile app depends on a mobile backend. Our application development process covers RESTful API design, Firebase and third-party SDK integration, and sync logic.

App Store & Google Play Store Launch

App Store and android google play store submission is a process, not a button. We handle metadata, screenshots, privacy compliance, and app store optimization for both stores.

Mobile App QA & Performance Testing

Mobile app performance regressions show up on real mobile devices — not just in CI. We test across android and iOS hardware so crashes, jank, and battery drain are caught before users do.

Mobile App Support & Maintenance

Post-launch mobile app development services keep products alive across OS updates and store policy changes. Our post-launch support covers monitoring, patches, and mobile platform upgrades.

Why Businesses Outsource Mobile App Development?

Space To Tech helps businesses reduce development costs, access specialized mobile expertise, and launch high-quality apps faster.

01

Cost Advantage Without Compromising Quality

India-based mobile developers typically work at $20–$45 per hour. Equivalent experience in the US or UK costs $100–$180 per hour. For a six-month mobile build, that difference funds additional engineering, QA, or product iteration.

02

Real Device Testing Infrastructure

Space To Tech maintains a device lab covering a range of Android manufacturers, OS versions, and screen configurations, plus the current iPhone and iPad lineup — not just emulators.

03

Production-Ready Quality Assurance

Mobile app development services that skip real-device validation produce apps that work in demos and break in production. We test on hardware users actually carry.

04

Structured Delivery Process

The question is not where the code is written. It is whether the process is structured enough that you always know what is being built, when it will be ready, and what happens when something changes.

Mobile App Development Services for Teams Globally

We build custom mobile applications for businesses worldwide, adapting to different industries, operational needs, and growth objectives.

World map

INDIA

India offers one of the largest mobile developer talent pools globally — full-stack mobile teams, UPI and payment gateway integration, and GST compliance logic built into fintech and consumer apps. For businesses outsourcing mobile app development, India combines delivery speed with the device-testing depth that fragmented Android hardware demands.

Ready to Build Your Mobile App?

✓Custom iOS & Android App Development
✓Native & Cross-Platform Solutions
✓Intuitive UI/UX Design & Prototyping
✓App Store & Google Play Deployment
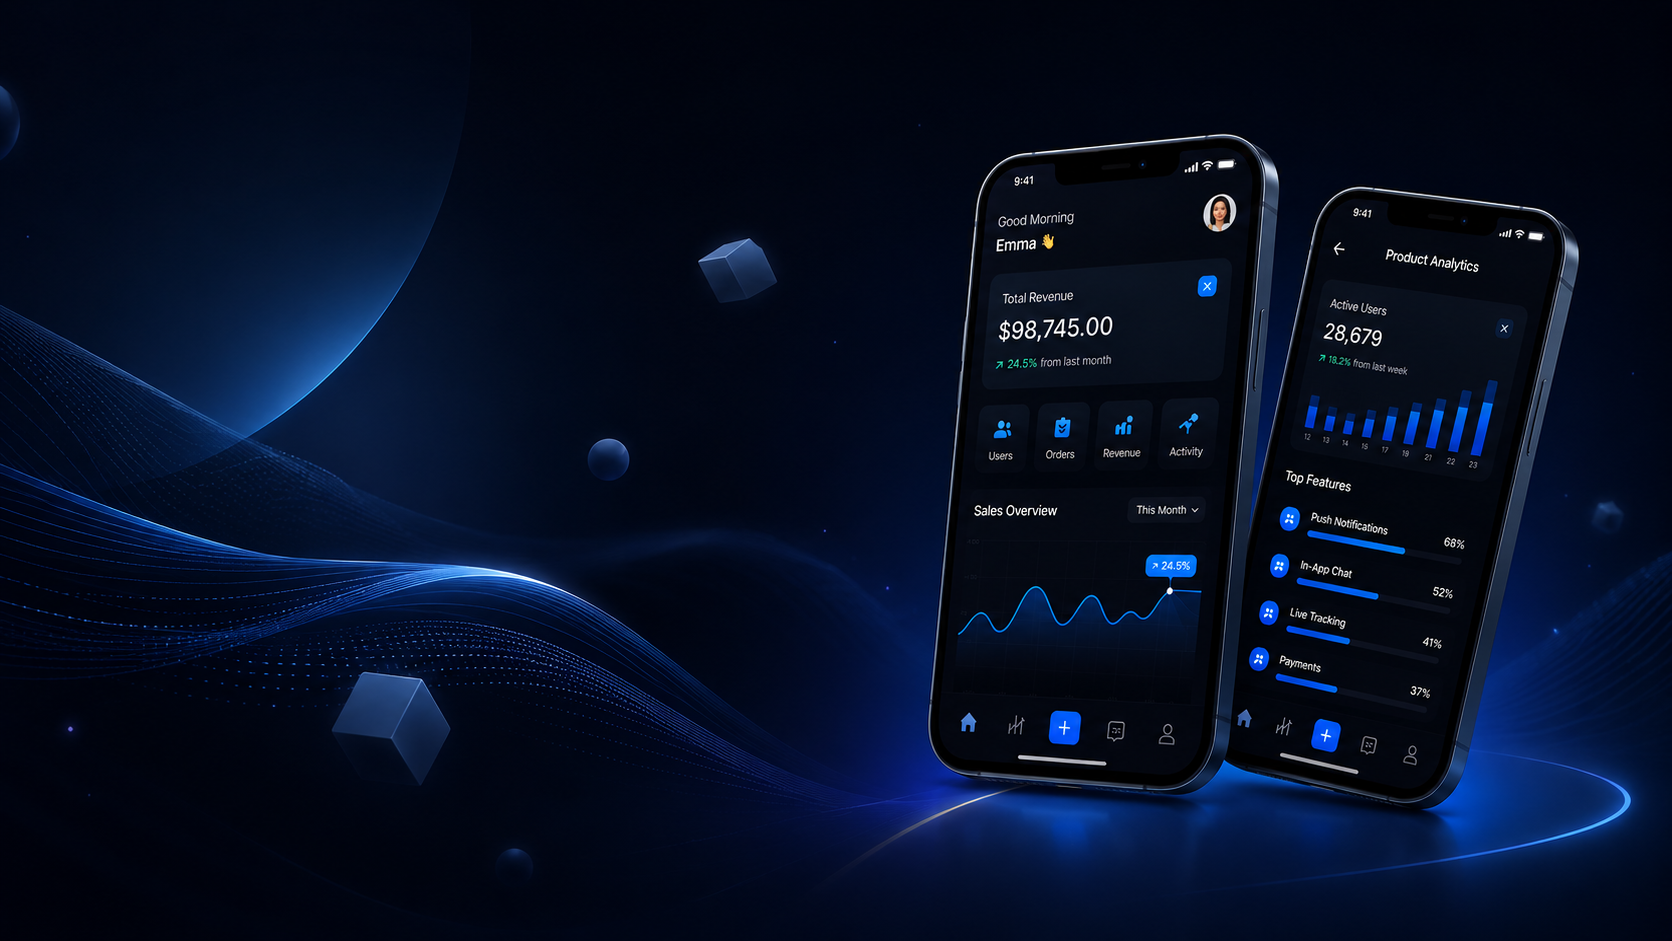
Mobile app showcase

Industries We Serve

Industry-specific mobile app development experience helps build solutions that align with real user needs, business goals, and market expectations.

FinTech & Payments

Real-time transaction tracking, biometric authentication, Google Pay / Apple Pay integration, PCI-DSS compliant payment flows

How Much Does Mobile App Development Cost?

This is usually one of the first questions clients ask. It should be. Budget discussions are far more productive when everyone starts with realistic expectations.

Basic Mobile App

Single function, simple UI

$5,000 – $12,000

MVP Mobile App

Core feature set, app store ready

$10,000 – $25,000

Mid-Complexity App

Multiple modules, API integration

$20,000 – $50,000

Advanced Mobile App

Real-time, payments, custom backend

$40,000 – $90,000+

Enterprise Mobile Application

Complex workflows, security, scale

$60,000 – $150,000+

eCommerce Mobile App

Catalog, cart, checkout, payments

$20,000 – $60,000

Cross-Platform App

React Native / Flutter

$15,000 – $45,000

Dedicated Mobile Developer

Monthly retainer

$2,500 – $6,500/month

Feature complexity, the number of API integrations, platform targets (iOS only, Android only, or both), and UI depth all influence where a project lands in these ranges. Backend requirements and App Store / Google Play submission preparation—including signing, policy compliance, and device-matrix testing—shape cost as much as screen count. We scope every engagement after mapping these drivers, not guessing from a generic hourly rate.

Hire Dedicated Mobile App Developers

Space To Tech offers three engagement models, each suited to a different type of product need.

Dedicated Mobile Developer

One or more developers working exclusively on your project, following your sprint schedule, using your tooling, and available through your communication channels. Best for long-term mobile builds and actively evolving roadmaps.

Flexible models. Complete transparency. Built for your success.

App Store & Google Play Launch Strategy

0101

App Store & Google Play Submission

Submission is a process, not a button. Both stores have metadata requirements, review guidelines, privacy policy mandates, and screenshot specifications that, if handled carelessly, result in rejections that delay launch by days or weeks.

0202

App Store Optimisation (ASO)

ASO affects how many users find the app organically after launch. The title, subtitle, keyword fields, and description are all ranking factors in both stores. Space To Tech treats ASO as part of the launch work, not an afterthought.

0303

Privacy & Compliance Support

We handle submission preparation for both platforms — keyword research and metadata optimisation, screenshot and preview design, privacy policy compliance checks, and the review response process when Apple or Google raises questions.

0404

Post Launch Monitoring

After the app goes live, crash monitoring, performance regression alerts, and user review tracking are active from day one. Launch is when real usage begins — and when backend, performance, and store visibility all need to hold up together.

Clutch 5.0 rating

Recognized. Trusted. Preferred

Awards & Recognition

We are proud to be recognized by leading platforms and industry experts for our innovation, impact, and excellence

TopDevelopers

TopDevelopers

Top Mobile App Developers

Freelancer

Freelancer

Top Mobile App Developers

AppFutura

AppFutura

Top Mobile App Developers

GoodFirms

GoodFirms

Top Mobile App Development

Clutch

Clutch

Top Mobile App Developers

Excellence isn't claimed.It's recognized

These achievements reflect our commitment to
delivering world-class AI solutions that help
businesses grow and lead

FAQs

What does a mobile app development company do?
A mobile app development company designs and builds applications for iOS and Android — including native apps, cross-platform apps, UI/UX design, backend and API integration, app store submission, and ongoing maintenance. Space To Tech handles the full lifecycle from architecture and development through launch and post-release support.
How much does mobile app development cost in India?
Mobile app development cost in India typically ranges from $5,000 for a basic app to $150,000+ for enterprise-grade products. India-based rates run $20–$45 per hour compared with $100–$180 per hour in the US and UK. Final cost depends on complexity, number of platforms, API integrations, and design scope.
What is the difference between native and cross-platform mobile apps?
Native apps are built specifically for one platform — Swift for iOS, Kotlin for Android — delivering the best performance and full access to device features. Cross-platform apps use frameworks like React Native or Flutter to share one codebase across iOS and Android, reducing time and cost when both platforms are required.
Should I build for iOS or Android first?
It depends on your target audience. Android holds 70%+ global market share; iOS users tend to have higher average spend and dominate the US and UK markets. If you need both platforms quickly, React Native or Flutter let you launch on iOS and Android simultaneously from a shared codebase.
How long does mobile app development take?
A simple app typically takes 6–10 weeks. Mid-complexity products need 12–20 weeks. Full enterprise apps often require 24–40 weeks. App store submission adds another 1–3 weeks for review on both the App Store and Google Play.
What is mobile app fragmentation and why does it matter?
Mobile app fragmentation refers to Android running on thousands of device models with different screen sizes, OS versions, and hardware capabilities. A serious mobile development company tests across this range as standard — not as an optional add-on — so apps perform reliably for real users, not just in demos.
Can I hire a dedicated mobile app developer from India?
Yes. Space To Tech offers dedicated developer, team augmentation, and project-based engagement models. Engagements include sprint reviews, NDA protection, full codebase access, and app store account ownership retained by you as the client.
What is ASO (App Store Optimization) and do you handle it?
ASO (App Store Optimization) is the process of optimizing your App Store and Google Play listing — title, description, screenshots, and keywords — to improve organic discoverability. Space To Tech handles ASO as part of the launch process, not as an afterthought once the app is already live.
Do you build AI-powered mobile apps?
Yes. Space To Tech builds mobile apps with AI features including recommendation engines, natural language interfaces, on-device ML inference, and AI-assisted personalization layers — integrated into production-ready mobile products, not proof-of-concept demos.
What industries does Space To Tech build mobile apps for?
We build mobile apps for FinTech, eCommerce, healthcare, logistics, EdTech, gaming, on-demand services, real estate, social networking, and enterprise tools — delivering projects for clients globally.

Supporting Insights

Website security checklist graphic showing a shield with pre-launch and post-launch checks around a browser window
Blogs23/10/2026

Website Security Checklist: 20 Checks Before and After Launch

A website security checklist is only useful if it tells you what to do before the site goes live and what to keep doing once it is public. Most lists skip that split, which is how launches end up with default passwords, a public staging site and nobody watching the logs. This guide gives you 20 checks, ten for before launch and ten for after, with a plain way to confirm each one is done and a note on who should do it. Security is one part of the wider picture in our web development guide , so treat this page as the deep dive for protection. It is written for owners and decision-makers who commission websites and web apps, not for security specialists. Quick answer: Before launch, enforce HTTPS, set security headers, validate every input, protect sessions, lock down logins and permissions, keep secrets out of code, scan dependencies, secure your APIs and test everything. After launch, patch on a schedule, test your backups, add a firewall, scan for malware, monitor logs, review access, manage certificates and domains, audit regularly, plan for incidents and keep compliance current. Who Is Responsible for Website Security? The short answer is that everyone involved owns a piece, and trouble starts in the gaps between them. A development team can build a solid login system, but if the owner never removes a former employee's admin account, the door stays open.  Party Usually owns Ask them for  Business owner Admin accounts, user access, domain and registrar logins, compliance decisions, budget Current user list, registrar details, renewal dates  Development team Secure code, authentication, API design, dependencies, testing, deployment Test summary, scan reports, update plan  Hosting provider Server hardening, network firewall, platform patches, infrastructure backups Backup policy, firewall coverage, uptime record Put these roles in writing before the project starts. Decide who patches, who monitors and who responds when something breaks. If you are hiring a web application development team , ask them to confirm in the proposal which of the checks below they handle and which stay with you. How to Use This Website Security Checklist Every check carries two tags. Priority is Critical, Important or Good practice. Owner is Owner, Developer or Shared. Start with the Critical items, because those are the ones attackers find first. The number of Critical checks grows with the complexity of what you run. A brochure site with a contact form has a small attack surface. A customer portal with logins, payments or stored personal data has a large one. If your project includes any of those, treat it as a web application, and read how a website differs from a web application before you decide how much testing to buy. Each check ends with a short "How to verify" line. You do not need to be technical to use it. You only need to ask for the evidence. Before Launch: 10 Security Checks These ten checks belong in your launch gate. If a check fails, fix it before the site is public. 1. Enforce HTTPS Everywhere With HSTS Priority: Critical | Owner: Developer HTTPS encrypts traffic between visitors and your server, and it is the baseline for any site that handles logins or forms. Redirect every HTTP request to HTTPS, use a current TLS version and add the Strict-Transport-Security header so browsers refuse to connect over plain HTTP in the future. A padlock alone does not make a site secure, but its absence makes every other check pointless. How to verify: Type your address with http:// and confirm it redirects. Run the domain through a free SSL test and look for a clean grade. 2. Set Security Headers Priority: Important | Owner: Developer Security headers tell the browser how to treat your pages. A Content Security Policy limits which scripts can run, which blunts many cross-site scripting attacks. Other headers stop your pages from being framed by other sites, stop browsers from guessing file types and control what referrer data you leak. They are cheap to add and often forgotten. How to verify: Run your domain through a free security headers checker and review anything marked missing. 3. Validate Every Input and Encode Every Output Priority: Critical | Owner: Developer Any field a visitor can type into is a possible attack route. SQL injection and cross-site scripting both start with the application trusting input it should have checked. Validation has to happen on the server, because checks that live only in the browser are easy to bypass. This is the kind of work that sits in back-end development , so ask your team how they validate input and encode output at every point where user data is stored or displayed. How to verify: Ask for the validation approach in writing and for a scan or code review result that covers injection and scripting flaws. 4. Protect Sessions With CSRF Tokens and Secure Cookies Priority: Important | Owner: Developer Once someone logs in, the site tracks them with a session cookie. If that cookie can be read by scripts or sent over an insecure connection, it can be stolen. Mark session cookies as Secure, HttpOnly and SameSite, and add CSRF protection so another site cannot trick a logged-in user into submitting an action they never meant to take. How to verify: Open your browser's developer tools, look at the cookies and check the flags on the session cookie. 5. Lock Down Logins Priority: Critical | Owner: Shared Weak authentication is still one of the easiest ways in. Require strong passwords, add multi-factor authentication for admins and for any account that can see sensitive data, and limit repeated failed attempts so brute-force tools get nowhere. Store passwords with a modern hashing method, never in plain text. As the owner, your part is to use the protections you are given and never share one admin login across a team. How to verify: Try a weak password, then try several wrong passwords in a row, and confirm the system blocks or slows you down. 6. Apply Least Privilege and Role-Based Access Control Priority: Critical | Owner: Developer Every user should see and do only what their role needs. Broken access control sits at the top of the OWASP Top 10 , and it often looks mundane: a customer who changes a number in a web address and sees another customer's invoice. Define roles early, enforce them on the server for every request and keep admin functions on a separate, protected path. How to verify: Log in as an ordinary user and try to open admin pages and other users' records. Both should be refused. 7. Keep Secrets and Configuration Clean Priority: Critical | Owner: Developer API keys, database passwords and tokens do not belong in source code or public repositories. Store them in environment variables or a secrets manager, use different values for staging and production, and turn off debug mode before launch. Detailed error pages that show file paths or database details are a gift to attackers. How to verify: Ask the team to confirm that no secrets are in the repository history and that production has debug output disabled. 8. Scan Dependencies for Known Vulnerabilities Priority: Important | Owner: Developer Modern sites are built from many third-party packages, and each one can carry a published flaw. Scan your dependency list before launch, remove packages you do not use and lock versions so builds are repeatable. The framework and library choices behind your project matter here, which is why it helps to understand the technologies top web development companies use and how actively each one is maintained. How to verify: Request the dependency scan report and the plan for fixing anything it flags. 9. Secure Your APIs Priority: Critical | Owner: Developer If your site or app talks to a back end through an API, every endpoint needs its own protection. Require authentication on each one, check permissions per request, validate the shape of incoming data, limit request rates and return only the fields the client needs. Mobile apps that share the same back end inherit the same risks, so the guidance in our mobile app security article applies to the client side of the same system. How to verify: Ask for an endpoint list showing the access rule for each one, and confirm that unauthenticated requests are rejected. 10. Test Before You Ship Priority: Critical | Owner: Shared Run an automated vulnerability scan on the finished build, and add a manual test or a penetration test if the product handles payments, personal data or health records. Block your staging site from search engines and from the public, and restrict file uploads by type and size. Security testing is strongest when it is part of the delivery process rather than a last-minute step, which is how the stages in a custom software development guide are normally laid out. How to verify: Ask for the test summary and the list of open findings, each with an owner and a date. After Launch: 10 Security Checks Launch day is the start of the work. These checks keep the site safe as software ages, staff change and attackers adapt. 11. Patch on a Schedule Priority: Critical | Owner: Shared Unpatched software is a leading way sites get compromised, because attackers scan the web for known flaws the moment they are published. Agree a monthly update cycle for the CMS, framework, libraries and server operating system, with faster handling for urgent fixes. Test updates on staging first so a patch does not break checkout. How to verify: Ask for the update log showing dates and versions. 12. Back Up Using the 3-2-1 Rule and Test the Restore Priority: Critical | Owner: Shared Keep three copies of your data, on two different types of storage, with one copy offsite. A backup you have never restored is a hope, not a plan. Decide how much data you can afford to lose and how long you can be offline, then check that your backup schedule and restore time fit those limits. How to verify: Request the result of a recent restore test, not just proof that backups ran. 13. Add a Web Application Firewall and DDoS Protection Priority: Important | Owner: Developer or host A web application firewall filters malicious traffic before it reaches your application, and DDoS protection absorbs floods designed to knock you offline. Neither replaces secure code, but both reduce the noise and buy you time when something new appears. How to verify: Confirm which provider and rule set you use, and check whether blocked requests are logged. 14. Scan for Malware and Watch File Changes Priority: Important | Owner: Developer or host Scheduled malware scans and file integrity monitoring tell you when something on the server changes without a deployment behind it. Early detection turns a long clean-up into a short one. How to verify: Ask to see the scan schedule and the most recent report. 15. Log, Monitor and Alert Priority: Important | Owner: Shared Logs are only useful if someone reads them. Track failed logins, unusual traffic, server errors and changes to admin accounts, and send alerts to a named person. If you have no engineers to watch this, bringing in dedicated DevOps or security capacity through IT staff augmentation is often quicker than hiring a full team. How to verify: Trigger a test alert and confirm it reaches the right person. 16. Review Access Every Quarter Priority: Critical | Owner: Owner People leave, agencies rotate and contractors finish. Every account they held stays active until someone removes it. List everyone with admin, hosting, code repository and analytics access every quarter, remove what is no longer needed and confirm multi-factor authentication is on for the rest. How to verify: Compare the user list against your current team and vendors. 17. Manage Certificates, Domains and DNS Priority: Important | Owner: Owner An expired certificate throws a browser warning, and a hijacked domain can redirect every visitor. Turn on automatic certificate renewal, lock the domain at the registrar, protect the registrar account with multi-factor authentication and keep DNS access limited to people who need it. How to verify: Check expiry dates for the certificate and the domain, and confirm who can change DNS records. 18. Schedule Regular Audits Priority: Important | Owner: Shared Run a vulnerability scan every quarter and a penetration test at least once a year for anything handling sensitive data. Repeat the scan after major releases or infrastructure changes. A vulnerability scan is automated and finds known weaknesses. A penetration test is a manual attempt to break in and finds what the tools miss. How to verify: Keep dated reports and track each finding to closure. 19. Write an Incident Response Plan Priority: Critical | Owner: Shared Decide in advance who leads when something goes wrong, who talks to customers, how you roll back to a clean version and when you must notify regulators or affected users. A one-page plan that people have actually read beats a long document nobody opens. When you evaluate vendors, ask how they handle incidents, since it tells you a lot about how they work, and our notes on how to choose a web development company cover what to look for. How to verify: Walk through the plan once a year with a simple scenario, such as a compromised admin account. 20. Keep Privacy and Compliance Current Priority: Important | Owner: Owner Rules attach to the data you hold, not the size of your company. Collecting cards brings PCI DSS into play, serving EU visitors brings GDPR, and handling patient information brings HIPAA. Keep your privacy policy and cookie consent accurate, and map the types of data you collect to the rules that apply. Healthcare products carry extra requirements, which we cover in our guide to custom healthcare software development . If your site sits in a regulated sector, the evidence a partner can show matters as much as their promises. Our piece on website development agencies for regulated industries explains how to verify that evidence. How to verify: Keep a short record of what personal data you collect, where it is stored and which rule covers it. The Full Website Security Checklist Table Copy this table into your project plan and mark each row as done, in progress or not applicable. # Check Phase Priority Owner How to verify 1 HTTPS with HSTS Before Critical Developer HTTP redirects; SSL test grade 2 Security headers Before Important Developer Headers checker report 3 Input validation and output encoding Before Critical Developer Scan or code review result 4 CSRF protection and secure cookies Before Important Developer Cookie flags in dev tools 5 Strong logins and MFA Before Critical Shared Weak password and lockout test 6 Least privilege and role-based access Before Critical Developer Standard user blocked from admin 7 Secrets and configuration Before Critical Developer Repository and environment review 8 Dependency scanning Before Important Developer Scan report and fix plan 9 API security Before Critical Developer Endpoint access list 10 Pre-launch testing Before Critical Shared Test summary and open findings 11 Patch schedule After Critical Shared Update log 12 3-2-1 backups with restore tests After Critical Shared Restore test result 13 Firewall and DDoS protection After Important Developer or host Provider and rule set 14 Malware scans and file monitoring After Important Developer or host Scan schedule and report 15 Logging, monitoring and alerts After Important Shared Test alert received 16 Quarterly access review After Critical Owner User list versus team 17 Certificates, domain and DNS After Important Owner Expiry dates and registrar lock 18 Scheduled audits After Important Shared Dated scan and test reports 19 Incident response plan After Critical Shared Yearly walkthrough 20 Privacy and compliance upkeep After Important Owner Data and rules record What to Do If Your Website Is Hacked Stay calm and work in order. Speed matters, but so does not destroying evidence. Contain it. Take the site offline or put it in maintenance mode, and disable compromised accounts. Preserve evidence. Save logs and take a copy of the affected files before you clean anything. Restore from a clean backup. Rebuild from a version you trust, then apply every pending update before going live again. Rotate every credential. Change passwords, API keys, database logins and tokens, not just the one you think was stolen. Notify and review. Tell affected users and regulators where the law requires it, then find the root cause and close it. Common Website Security Mistakes Launching with default or shared credentials. Admin and database logins should be unique and stored in a password manager. Leaving the staging site public. Test environments often hold real data and weaker settings. Treating HTTPS as the finish line. Encryption protects data in transit, not a vulnerable application. Postponing updates. A patch delayed by a few weeks is often the whole story behind a breach. Never testing a restore. Many teams find out their backups are incomplete only when they need them. Conclusion A website security checklist earns its place by turning vague worry into specific jobs with owners and evidence. Get the ten launch checks right so you ship with a solid foundation, then run the ten ongoing checks on a calendar so the foundation does not erode. Agree who owns each one, keep the proof, and rehearse your incident plan before you need it. If you are planning a new build or want a second opinion on an existing one, the team at SpaceToTech builds secure web applications with these checks built into delivery. You can talk to us about your project , and we will walk through what your site needs.

Cost to Hire a Web Developer in India
Blogs23/10/2026

Cost to Hire a Web Developer in India: Real Rates, Budgets and Pitfalls

Asking what it costs to hire a web developer rarely produces one clean number, because location, seniority and the way you engage the person all move the price. In India, rates run from a few dollars an hour for a junior freelancer to $50 or more for a senior engineer at an agency, and the cheapest quote is not always the lowest total cost. This guide breaks down hourly, monthly and project pricing, explains what shifts each figure, and flags the pitfalls that turn a bargain into expensive rework, so you can budget with confidence before you brief anyone. What the Cost to Hire a Web Developer in India Looks Like India has two price lists. Rates quoted in rupees for domestic work sit below the dollar rates quoted to overseas clients through agencies and platforms. Published estimates for hiring developers in India put the range at roughly $20 to $50 per hour. A wider market survey places full-stack web developers at about $25 to $55 per hour depending on stack and seniority. For context, senior developers cost about $100 to $150 an hour in the US and $80 to $120 in the UK, against $25 to $40 in India. Treat every figure below as an indicative 2026 range, not a quote. Use the band that matches how you will actually buy. Cost to Hire a Web Developer per Hour Hourly billing suits work with an unclear scope, such as maintenance, audits or feature additions. Freelancers cost less per hour than agencies because agency rates include project management, QA and overhead. Experience level Freelancer (per hour)  Agency (per hour) Junior (0 to 2 years) ₹300 to ₹700 ₹700 to ₹1,200 Mid-level (3 to 5 years) ₹700 to ₹1,500 ₹1,200 to ₹2,200 Senior or lead (6+ years) ₹1,500 to ₹3,000  ₹2,200 to ₹4,000 At roughly ₹85 to ₹90 to the dollar, most Indian agency rates land between $15 and $50 an hour. Outside benchmarks vary more. One source puts freelance rates in India at about ₹600 to ₹2,500 per hour, or roughly $7 to $30. Another reports that a mid-level freelance or contract developer costs $20 to $52 an hour. Gaps like these usually reflect who is quoting and to whom, not an error. Freelancers also tend to run roughly half the hourly rate of an India-based agency for the same scope, but without the process around them. Cost to Hire a Web Developer per Month Monthly pricing applies when a developer works for you full-time, either in-house or on a dedicated basis through a vendor. A dedicated developer from an agency typically costs about ₹60,000 to ₹2,00,000 per month , depending on seniority. Outside estimates are wider. One guide shows a mid-level web or e-commerce developer at roughly $1,500 to $2,500 a month through a dedicated-developer provider. Another puts a dedicated engineer at about $2,500 to $8,000 a month, depending on stack and channel. A quick check: a freelancer billing 160 hours a month at $20 to $50 an hour comes to $3,200 to $8,000. That is why full-time monthly rates through a vendor often look cheaper than stacking up hourly freelance bills. The monthly figure bundles a commitment, so you pay for availability as well as output. Engagement Typical monthly cost Notes Dedicated developer via agency  ₹60,000 to ₹2,00,000 Replacement and oversight usually included Freelancer, full-time hours ₹1,12,000 to ₹4,80,000 (160 hrs, mid to senior) You manage the work and the risk In-house employee Salary plus recruitment, equipment, benefits Web roles run about $8,000 to $22,000 a year in salary alone Hiring Models That Set the Price The same developer can cost very different amounts depending on how you engage them. The cheapest model on paper is not always the cheapest once your management time and rework are counted. Freelancer, In-House Developer or Agency Freelancer. Best for small, well-defined tasks and tight budgets. You manage the work directly, and continuity depends on one person. Quality varies, so review live projects and speak to past clients before committing. In-house developer. Best when web development is a continuous, core function. Budget for recruitment, equipment, benefits and management time on top of salary. The all-in annual cost is well above the salary figure. Agency. Best for projects needing several skills, fixed dates and accountability. You pay a premium for project management, QA and redundancy, and you get one party responsible for delivery. An agency usually earns that premium when the site is business-critical or when you lack internal capacity to manage technical work. It is rarely worth it for a one-page site or a quick template change. If agency pricing is your main question, our breakdown of web development companies in India compared by cost shows how enterprise, mid-size and boutique tiers differ. When to Hire Web Developers on a Dedicated Basis A dedicated model sits between freelancing and building a team. An agency supplies developers who work exclusively on your product, under your direction, with the vendor handling HR, replacement and review. It suits products with a continuous roadmap and an evolving backlog. It works best when the developer joins your tools and has real time-zone overlap, you interview the actual person rather than "the team", and your contract names IP ownership, hours, rate and reporting. For a step-by-step view, read our guide on how to hire software developers from India , or look at how IT staff augmentation works in practice. Skills and Seniority Behind a Web Developer's Rate "Web developer" covers several roles with different price points. Naming the role you need is the quickest way to get comparable quotes. Front-End, Back-End and Full-Stack Roles Front-end developers build what users see and touch: layouts, interactions, responsiveness and performance. Back-end developers build servers, databases, APIs and business logic. Full-stack developers cover both, which is why they usually cost more per hour but can reduce the number of people on a small project. To see how these roles map to project types, review the main types of web development . Annual cost benchmarks reflect the split. One 2026 guide lists front-end specialists at about $8,000 to $18,000 per year, back-end at $10,000 to $20,000 and full-stack at $12,000 to $22,000. Treat these as in-house salary indicators, not what an agency will bill you. Experience Level and Technology Stack Seniority moves the rate more than any other lever. A senior developer costs more per hour, but may finish in fewer hours and make fewer architectural mistakes. A $15 hour and a $55 hour are not the same product at two prices. The difference shows up in code quality, testing habits and how much supervision the work needs. Technology stack matters too. Common stacks such as WordPress, Shopify or React with a headless CMS have large talent pools and predictable pricing. Niche frameworks, legacy migrations and specialist skills command a premium because fewer developers can maintain them. Before you approve a stack, compare it with the technologies used by top web development companies so you are not paying a premium for something unusual. Project-Based Pricing by Website Type Fixed-price quotes give budget certainty when the scope is detailed and change requests are priced upfront. These ranges are indicative for 2026. Project type Typical range (INR) Typical timeline Brochure or small business website ₹40,000 to ₹2,00,000 2 to 5 weeks Corporate website with CMS and SEO setup ₹1,50,000 to ₹5,00,000 4 to 10 weeks E-commerce store ₹3,00,000 to ₹15,00,000 8 to 16 weeks Custom web application or portal ₹8,00,000 to ₹40,00,000+ 3 to 9 months Business Websites and Online Stores For a standard business site, the main cost drivers are the number of page templates, how custom the design is and which CMS you choose. A site built on a modified theme costs far less than one with a bespoke design system. Online stores add payment gateways, inventory, shipping rules and checkout testing. Each integration needs design, build and QA time, and pricing only the visible pages is the most common budgeting mistake. If you are planning a store or a shopping app, our e-commerce app development cost guide goes deeper on those line items. Custom Web Applications A web application, with user accounts, dashboards, workflows and data, is a different project from a website. Cost scales with the number of user roles, integrations, security needs and expected load. If you are unsure which one you need, our website vs web application comparison explains the difference. The distinction can change a budget by an order of magnitude. Hidden Costs and Pitfalls to Avoid The quote is the visible part of the bill. The pitfalls below explain why two honest quotes for the same brief can differ tenfold, and why the cheapest one sometimes ends up the most expensive. Costs That Sit Outside the Quote Hosting, domain and licences: cloud hosting, premium plugins, themes, fonts and paid APIs usually sit outside a development quote. Integrations and content migration: payment, CRM, ERP and multilingual setups, plus moving content from an old site, often bring extra time. Quality and compliance work: cross-browser testing, accessibility checks and security hardening take effort that low bids tend to skip. Search and discovery setup: technical SEO, redirects, schema and Core Web Vitals work. As buyers increasingly use AI tools to research vendors and products, AI search visibility for e-commerce sites is worth budgeting for early. Maintenance: security updates, bug fixes and improvements continue after launch. A commonly cited rule of thumb is 15 to 20% of the build cost per year, but ask for a written estimate based on your own stack. Management time: freelancers and in-house hires need briefing, review and coordination. Your hours are part of the cost. Tax: Indian agencies usually add GST to domestic invoices, while overseas clients are often invoiced differently. Confirm with the vendor and your accountant. Red Flags in Proposals A price far below every other quote, with little detail on what is included. No discovery phase or requirements document before development starts. Reluctance to share references, live project links or the names of the people assigned to your build. Vague change-request rules that let costs grow unchecked. Pressure to sign quickly because of a "limited-time" rate. Hosting, domain or admin access held by the vendor without your consent. No clear statement that you own the source code, design files and content at payment. Claims of "full compliance" without documents. If your site handles health or financial data, see how website development agencies for regulated industries prove their record. One clear signal of a mature vendor is willingness to say "that is not worth building yet." A realistic budget, a clear scope and a vendor who will push back are better predictors of success than the lowest number on the page. How to Budget and Hire the Right Web Developer A structured approach beats comparing headline rates. Follow these steps in order. Define the scope before you ask for prices. Write down pages, features, user roles, integrations and launch date. The more specific the brief, the more comparable the quotes. Choose the engagement model. Hourly for uncertain work, fixed price for defined builds, monthly or dedicated for continuous roadmaps. Set a range, not a single figure. Use the tables above, add 15 to 25% for contingency, and keep a separate line for hosting, licences and maintenance. Send the same brief to three to five vendors. Compare how well each restates your problem, not only the price. Check evidence. Call two references, test live projects on mobile, and review code ownership and support terms in writing. Start small. A paid discovery phase or a short pilot sprint shows how the team works before you commit to the full build. When you reach the vendor stage, the best web development companies and the web development companies in India shortlist give you named options. For platform-scale or multi-discipline projects, compare partners using our list of the best custom software development companies . Conclusion The cost to hire a web developer in India is a range, and where you land in it depends on the role, the model and the scope you can define. Hourly rates suit uncertain work, monthly rates suit continuous roadmaps, and fixed prices suit well-specified builds. Whichever you choose, budget for the costs outside the quote, and protect yourself with written ownership, itemised scope and references. If you are ready to move from budget to vendor, start with the best custom software development companies in India and compare them against the criteria above. For a scoped estimate on your own project, you can book a free consultation with the SpaceToTech team. Related reading: Top website development companies in India | Top 5 web development companies in India | Web development company trends
Website Development Agencies
Blogs22/10/2026

Website Development Agencies for Regulated Industries: What Proven Success Really Looks Like

Choosing a web partner gets harder when your site must satisfy HIPAA, PCI DSS, FINRA or accessibility rules. Buyers researching website development agencies for regulated industries rarely want a generic list; they want to know which agencies have shipped compliant sites and can prove it. This guide explains what proven success looks like in healthcare, finance and other regulated sectors, which compliance standards shape the build, and how to verify an agency’s claims before you sign. It also covers agency types and documented examples so you can shortlist with confidence and bring a defensible choice to your legal and security teams. Website Development Agencies Built for Regulated Sectors A regulated-industry website is not a standard build with a compliance checklist attached at the end. Legal review, consent management, audit trails and accessibility obligations shape architecture decisions from the first sprint. Agencies that treat them as late-stage add-ons tend to hit the same problem: the project slips at approval, not at development. Because these decisions span front-end, back-end and infrastructure work, it helps to understand the main types of web development before you brief an agency. How Regulated-Industry Specialists Differ from Generalist Agencies Website development agencies with industry experience have usually seen the failure modes before. They know which form fields collect protected data, which marketing tags create exposure and how long a compliance sign-off realistically takes. A generalist agency can still deliver strong work, but then regulated expertise depends on the individual team assigned, so ask who will actually work on your project. A specialist typically brings: Component libraries and templates already reviewed against sector rules Working relationships with legal and compliance reviewers Experience answering vendor security questionnaires and due diligence Boutique, Full-Service and Offshore Engineering Partners Compared Agency type Strengths Trade-offs Boutique sector specialist Deep rules knowledge, senior teams, smoother approvals Narrower capacity, premium pricing, less engineering breadth Full-service agency Scale, integrated design, SEO and support under one contract  Regulated experience varies by team; slower and costlier to change Offshore or nearshore engineering partner Cost-efficient engineering capacity and flexible team size Needs strong governance: data residency, access controls, IP and compliance ownership must be written into the contract No model is universally best. The right choice depends on who owns compliance decisions inside your organisation and how much of the build is bespoke. If an offshore partner is on your list, our breakdown of web development agency costs in India shows what to expect on budget, and our guide to choosing a web development company covers the wider decision. Plan for the approval cycle as well as the build. Regulated projects usually include legal review of copy, privacy review of data flows and security sign-off before release, and each of these can send work back a step. An agency that has run this cycle before will schedule reviews early, keep a record of decisions and give you a realistic timeline instead of a best-case one. Regulated Industries Set the Compliance Bar for Every Website “Regulated” covers many sectors, and each regulator cares about different things on a public website. Knowing which rules apply to you is the first filter for any agency conversation. Healthcare and Finance: HIPAA, PCI DSS and FINRA Obligations In the United States, healthcare organisations must protect health information under HIPAA. For a website, that touches patient portals, appointment and contact forms, and any analytics or advertising tag that could pass identifiable health information to a third party. Website development companies for healthcare and finance should be able to explain where regulated data enters the site and where it must never go. Financial services add another layer. Sites that take card payments fall under PCI DSS, whose current version includes requirements to manage and monitor the scripts running on payment pages. Broker-dealers and investment firms must also treat website content as regulated communication, which brings review, approval and record-keeping duties under FINRA and SEC rules. Banks and credit unions face further expectations from their own supervisors.  [ HHS HIPAA Security Rule overview ]  [ PCI Security Standards Council, PCI DSS ]  [ FINRA Rule 2210, communications with the public ] Other sectors bring their own rules. Insurers, legal firms, pharmaceutical companies, energy providers and public bodies each answer to different regulators, and some face advertising and promotional-content controls that apply to every page. The practical lesson is the same in each case: write down the rules that govern your site before you brief an agency, because an agency can only design around constraints it has been told about. Compliant Website Development Beyond Sector Rules: Accessibility and Privacy Some obligations cut across every industry. Accessibility is the clearest: WCAG 2.2 is the benchmark most buyers and auditors reference, and complaints over inaccessible sites are a recurring legal risk. Privacy is the other. GDPR and comparable laws require a lawful basis, clear consent and honest cookie handling, which means a consent banner must actually hold tags back until a visitor agrees. Compliant website development treats both as design requirements, not final-stage fixes. [ W3C WCAG 2.2 recommendation ] Proven Success Is Verifiable, Not Claimed Every agency says it has experience. Proven success is different: it is evidence a third party could check. Treat the claim as a hypothesis and ask for the proof. Evidence to Request: Case Studies, Certifications and Audit Outcomes Compliance-focused website development services should come with an evidence pack. Ask for: Named case studies in your sector, with permission to speak to the client Current certifications or reports covering the agency’s own operations, such as SOC 2 or ISO 27001, including scope and date An independent accessibility audit of a delivered site Sample documentation: a threat model, release checklist and data-flow diagram References from clients whose site went through legal or regulatory review after launch Read certification wording carefully. A certificate covering an agency’s internal systems says little about the security of the site it builds for you, and “compliant infrastructure” is not the same as independently certified infrastructure. When you speak to a reference client, go beyond satisfaction. Ask whether the site passed legal and security review the first time, how many rounds of changes were needed, what the agency did when a requirement changed late, and whether the client would hire them again for a higher-risk project. Those answers show how the agency behaves under regulatory pressure, which is what you are really buying. Post-Launch Proof: Accessibility Conformance, Uptime and Incident Record Launch day is the easiest moment to look good. The better evidence comes later: whether the site still meets WCAG after a year of content changes, whether security patches shipped on schedule, and whether any incident was handled and disclosed properly. Ask for uptime history, patch turnaround times and how the agency dealt with its last security issue. A candid answer to that last question is a strong trust signal. Secure Website Development Starts Before the First Line of Code Secure website development for regulated industries is a process, not a plugin. Weak points usually appear in planning and integration, well before launch. Secure Delivery Practices: Threat Modelling, Pen Testing and Hosting Look for a secure development lifecycle: threat modelling during design, code review, dependency scanning and penetration testing before release. The OWASP Application Security Verification Standard gives buyers a shared vocabulary for testing an agency’s answers. Hosting matters as well. Ask where data is stored, how environments are separated, who holds production access and how that access is logged and revoked. Keeping the marketing site apart from systems that hold regulated records limits the damage if either side is compromised. If you are unsure where that line sits, our explainer on website vs web application shows how the two differ. Technology choices also shape your attack surface, so our overview of the technologies used by top web development companies is a useful reference when you review an agency’s proposed stack. [ OWASP ASVS ] Useful questions to put to any shortlisted agency about hosting and access: Where will production data and backups be stored, and in which jurisdiction? Which team members can reach production, and how is that access reviewed? How quickly are critical vulnerabilities in dependencies patched? What is the rollback and incident-notification process if something goes wrong? Third-Party Scripts, Analytics and Regulated Data Leakage The most overlooked risk is rarely custom code. Analytics tags, live chat widgets, session-replay tools and advertising pixels can send form entries, URLs or identifiers to outside vendors without anyone noticing. In a regulated sector that can amount to an unintended data disclosure. A capable agency will inventory every third-party script, load them only after consent, keep them off pages that handle sensitive data and re-audit them whenever marketing adds a new tool. Agencies with Documented Regulated-Industry Work The agencies below publicly describe regulated-industry web work. This is a starting point for research, not a ranking or endorsement. Details come from each agency’s own materials or trade-directory profiles, so verify them against the evidence list above before shortlisting. If location is a factor, our list of top web development companies in India covers India-based providers; the agencies below are chosen for sector focus rather than geography. Healthcare and Pharma Specialists Genetic Digital describes itself as a specialist digital agency for life sciences and pharma, building compliant websites, apps and digital tools for prescription medicines and medical devices, and says it has done so for more than two decades. UniWeb , based in Brussels and Riga, says it builds web and mobile applications for e-business and for the healthcare and pharma sectors, and has worked since 2000. Multi-Sector Compliance Agencies Covering Finance and Legal Custody & Agency , with offices in Syracuse, Dallas and San Diego, says it works within HIPAA, FINRA, ABA, PCI DSS and WCAG 2.2 frameworks and advertises SOC 2 compliant infrastructure; ask for documentation behind those claims. Illustrate Digital is a UK WordPress agency positioning itself around regulated markets, including government and charity organisations, with clients across Europe. Disclosure: SpaceToTech publishes this guide and is itself a web and software development provider. It is not ranked here, and this list is not exhaustive. Notice what these profiles have in common: each agency states a sector focus, names the frameworks it works to and has a track record that can be tested through references. That pattern, rather than any single brand, is what separates an agency with proven regulated-industry success from one that merely lists compliance among its services. A Practical Framework for Shortlisting the Best Agencies The best website development agencies for regulated industries are the ones that fit your risk profile, and only you can score that. For a broader vendor comparison beyond web projects, see our guide to best custom software development companies . A Weighted Scorecard for Comparing Agencies Criterion Weight What good looks like Regulated-sector experience 25% Named, referenceable clients in your sector  Security and compliance evidence 25% Dated SOC 2 or ISO 27001 scope, penetration testing, documented secure development process Accessibility record 15%  Independent WCAG 2.2 audit on delivered work Delivery and approval process 15% Workflow with legal and compliance sign-off built in Post-launch support 10%  Patch turnaround targets, monitoring, incident process Commercial fit 10% Transparent pricing and clear terms on IP, data and liability Adjust the weights to your situation. A payment-heavy site may weight security higher; a public-health site may weight accessibility. For market context on where agencies are heading, see our review of top web development companies trends . Red Flags and Questions to Ask Before You Sign Be wary of an agency that: Cannot name any client in your sector, or gives no reason why not Offers compliance claims without documents to back them Promises a site that is “fully compliant”; compliance is a shared responsibility, and no agency can deliver it alone Has no plan for third-party scripts or consent handling Will not name the people who will work on your project Then ask: Who on the team has delivered in my sector? How are regulated data and analytics handled in forms? What happens when legal rejects a design late? Who signs off on compliance decisions? A Simple Selection Process That Fits Compliance Reviews Run the search in stages so your legal and security teams are involved before a contract is signed: Shortlist three to five agencies using the scorecard and public evidence. Send each the same evidence request and requirements brief. Hold a technical workshop covering data flows, hosting and third-party scripts. Call two references per agency, using the questions above. Start with a paid discovery phase, so you can judge the working relationship before committing to the full build. Choosing a Partner Your Compliance Team Can Defend Choosing among website development agencies for regulated industries comes down to evidence you can check, not promises. Define the rules that apply to you, ask for proof in your sector, test the agency’s security habits and score each shortlisted partner on the same criteria. The result is a decision your legal, security and marketing teams can all stand behind. If the project extends beyond the website, apply the same criteria when choosing a custom software development partner .
We’ve been helping Customer globally

So how does it work? Check for yourself by their feedback.

Client Feedback

We Build Digital Products That Drive Real Growth

From idea to launch, we help startups and enterprises build scalable apps, AI solutions & custom software.

View Our Work
Trusted byGlobal Clients

150+Projects Delivered

OngoingSupport
UAE

UAE

USA

USA

INDIA

INDIA

Book a Free Consultation

Your information is safe with us.